A Trusted Network: The Internet I Want My Children to Inherit
October 24, 2026 1 Comment
I want my children to inherit the freedom I found on the Internet, without inheriting the fear we have learned to treat as normal.
I have spent much of my working life arguing for a network in which someone unknown can arrive, contribute, and matter. That conviction has shaped my research, my writing, and how I think about business. The most consequential person in a network might be the one who has not joined it yet.
In “Black October Broke the Internet’s Social Contract. Now We Must Decide What Replaces It,” I recently examine the major choices this moment has put before us: How to rebuild trust while preserving the precious openness that made the Internet extraordinary.
Since writing it, I keep thinking about the world on the other side of that decision. What will my children be able to explore? What will they be able to create? Will an unfamiliar person still represent the possibility of a new friend, collaborator, or discovery?
Those questions take me back to the beginning, because the Internet has repeatedly become something greater when we have widened the possibilities of participation.
The future was there at the beginning
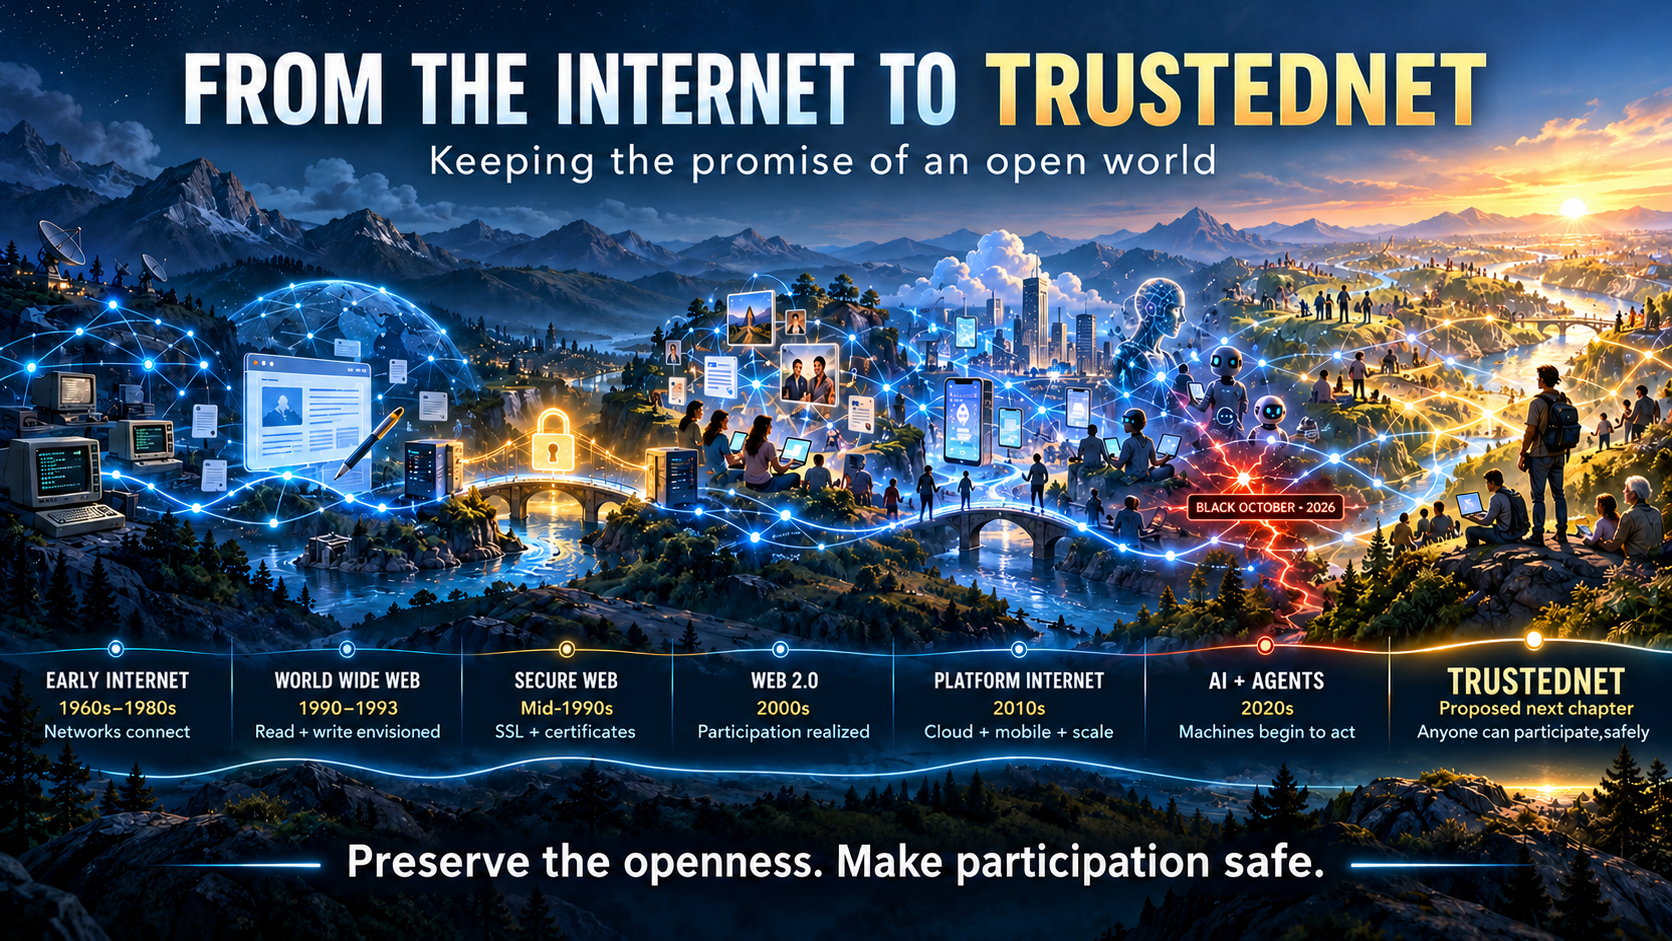
The Internet and the Web arrived in different chapters. The Internet grew out of relatively small, restricted research communities, around an architecture that let independent networks communicate through shared rules. ARPANET’s transition to TCP/IP in January 1983 was one decisive step in that longer history. The underlying achievement was extraordinary: Different systems could become part of a larger whole without becoming the same system.
Then Tim Berners-Lee gave that connected world the Web.
His first browser, written in 1990, was also an editor. Creating belonged alongside reading from the start. In 1993, CERN put the Web software into the public domain, helping make it something the world could adopt and build upon. Openness was a deliberate choice, with consequences far beyond the people making it.
Yet the early popular Web developed largely as a publishing medium. Organizations put up pages, and most people experienced the Web primarily as visitors. Berners-Lee himself observed in 1996 how far that predominantly read-only experience had drifted from his original vision of an interactive, shared information space.
However, that possibility was ahead of our habits.
Learning to trust the connection
Then another great pivot came in the mid-1990s, as SSL and digital certificates gave browsers a practical way to encrypt connections and authenticate the server at the other end. That helped make online commerce viable. TLS, SSL’s successor, carried that work forward and is what we use today to conduct important work safely.
The browser’s little padlock became part of everyday life. Its actual promise was limited: A protected connection to a single site. It could not guarantee that the business was honest, the software harmless, or the content true. The distinction remains essential; namely that browser security teams have spent years trying to correct the belief that a padlock certifies a trustworthy website.
Even so, this was a remarkable expansion of what people could reasonably attempt online. We added protection to a shared network and opened up new possibilities. That history matters now. Greater safety has helped the Internet grow before.
When participation finally became ordinary
By the middle of the 2000s, the next shift was unmistakable, and many of you know, I was there for it. People were publishing blogs, building wikis, sharing photographs and video, and forming communities around almost anything imaginable. The audience was helping create the place.
On September 4, 2006, I wrote “All We Got Was Web 1.0, When Tim Berners-Lee Actually Gave Us Web 2.0.” My argument was that the participatory vision had been there much earlier. What took time was the arrival of enough people with the tools, confidence, skills, and habits to make it real. Better technology helped. Changes in human behavior gave it scale. Web 2.0 was the moment that possibility became an everyday practice.
Looking back twenty years later, I am struck by how much of the Internet’s history follows that pattern. A technical possibility becomes a human capability. People discover what they can do together. Institutions struggle to catch up. I still regard this as historic and a monumental achievement, and I still believe it is worth defending very vigorously.
The late middle age of the Internet
Today, I think the current Internet has entered late middle age. It is accomplished, indispensable, and burdened by its history. We have made it the setting for our work, our commerce, our relationships, and much of our collective memory.
We have also made participation increasingly difficult to separate from exposure. Black October has sharpened a question I can no longer put aside: How much responsibility can we reasonably place on each individual to survive in an environment this complex?
The parent, the teacher, the independent publisher, and the small business owner cannot each become experts in every institution and technology on which their digital lives depend. The principle I have defended for so long now demands more of us. I care deeply about whether people are free to participate. I also have to ask whether they can safely exercise that freedom.
A person who is too frightened to contribute, too vulnerable to withstand a mistake, or too exhausted to keep defending themselves has little practical use for a theoretical right to join., No, safety is now part of making openness real.
What I mean by TrustedNet
I increasingly believe we need a new Internet: A substantial renewal of the network’s foundations and the expectations we can reasonably have of it. The name “Internet” describes the original accomplishment of connecting networks. Our next great accomplishment must be making that connected world dependable enough for the lives we now live within it.
For now, I would call it TrustedNet. That is a working name for a public ambition: A network whose protections, boundaries, and institutions ordinary people can reasonably rely on. Its safeguards would have to work even when a participant deceives us, an authority fails, or someone makes a mistake. The name would be a promise to earn continuously.
TrustedNet must grow within and alongside the Internet we already have. Its task is to carry forward the knowledge, communities, relationships, and freedom accumulated there, while changing the conditions under which we participate.
The central requirement is one I have held for a long time. In Social Business By Design, which I wrote with Peter Kim in 2012, our first tenet was simple: “Anyone can participate.” I meant it then. I mean it now. If TrustedNet breaks that principle, it is not worth having.
The principles I would start with
Anyone can participate.
A newcomer must have a practical way to read, publish, contribute, and build without an institutional sponsor, an expensive credential, or a reputation they have never had the opportunity to earn. Being unknown must leave room for possibility. Affordable access, accessible tools, and ordinary devices have to be part of the design.
People decide what others may do.
Public information should remain discoverable, and new relationships should remain possible. Access to someone’s money, private information, or systems should depend on permission appropriate to the action. People must be able to understand and withdraw that permission. Anyone can participate and each of us still gets to have boundaries.
Privacy is part of safety.
People should be able to explore, speak, and contribute without exposing their entire identity or history. A particular transaction may require stronger proof. That must never become an automatic demand for a permanent identity record of everyone’s ordinary life. Pseudonyms and private conversations have a legitimate place in a trustworthy world.
Protection must be ordinary.
A family, school, or small business should receive useful protection by default. Basic safety must be affordable and understandable without a security department. We should measure progress by how well ordinary people can participate with confidence, including those with the fewest resources to defend themselves.
No one gets to own participation.
The essential rules must be open, different providers must work together, and people must be able to leave one provider without abandoning their digital lives. Independent builders need a real opportunity to offer alternatives. No company or government should become the permanent admissions office for human connection.
Trust must answer to people.
The institutions that establish trust must themselves face scrutiny. Restrictions need understandable reasons and meaningful ways to challenge mistakes. Trust should be specific to a relationship or action. Nobody should be reduced to a universal score that determines where they are allowed to belong.
Failure must be survivable.
Devices will be compromised. Credentials will be stolen. Institutions will make mistakes. Damage must be contained, and people must have a workable way back. Losing an account or a device should not mean losing one’s place in the world. Recovery belongs among the network’s basic promises.
Bring the existing Internet with us.
Old links, independent websites, archives, communities, and useful services deserve a credible path forward. Adoption must deliver benefits gradually, while people remain connected to those who have not yet moved. Older systems will need protection and repair. Preserving our shared past also requires making it safer to carry into the future.
These principles are demanding. They should be.
The test is whether more people can participate with confidence, including the people easiest to overlook: the newcomer, the dissenter, the person with little money, the small organization, and the child just discovering what the world contains.
The hardest thing we may ever do
There is a formidable difficulty here, and it comes from the very quality I have spent years celebrating: Network effects.
The Internet’s value lives in the people, organizations, knowledge, and relationships already connected through it. A better network is of limited use if your family, customers, colleagues, and communities remain somewhere else. We cannot ask humanity to leave its relationships behind and start again.
That makes this a different undertaking from inventing a network for a small community of researchers. We must change a system on which the world already depends, while keeping that world connected. We must make it safer without handing permanent control to those best positioned to sell safety. We must find agreement across institutions and nations whose interests frequently conflict.
Given the immense network effects now binding us to the Internet, I suspect fixing it will be the hardest thing we ever do in technology. There will be costs, compromises, and years of uneven progress. Some of the hardest changes will concern power: who gets to establish trust, who can withdraw it, who pays to sustain it, and what recourse the rest of us have when they get it wrong.
A new name cannot settle those questions, but it can help us state the obligation clearly. And the history gives me hope. People chose to make different networks work together. People chose to make the Web available for others to build upon. People learned to contribute to something that had initially offered them mostly pages to read. People made it relatively safe to use (for the time.)
I still believe in the person we have never heard of, arriving with an idea we did not anticipate. I want my children to be able to be that person or readily encounter that person. And I want them to have a reasonable expectation that reaching out will lead to possibility.
The Internet gave us an extraordinary way to find one another. A new TrustedNet should make that freedom safe enough to keep.